Submitted by: Bethney Seifert, State Regent
Dear NSSDAR Members,
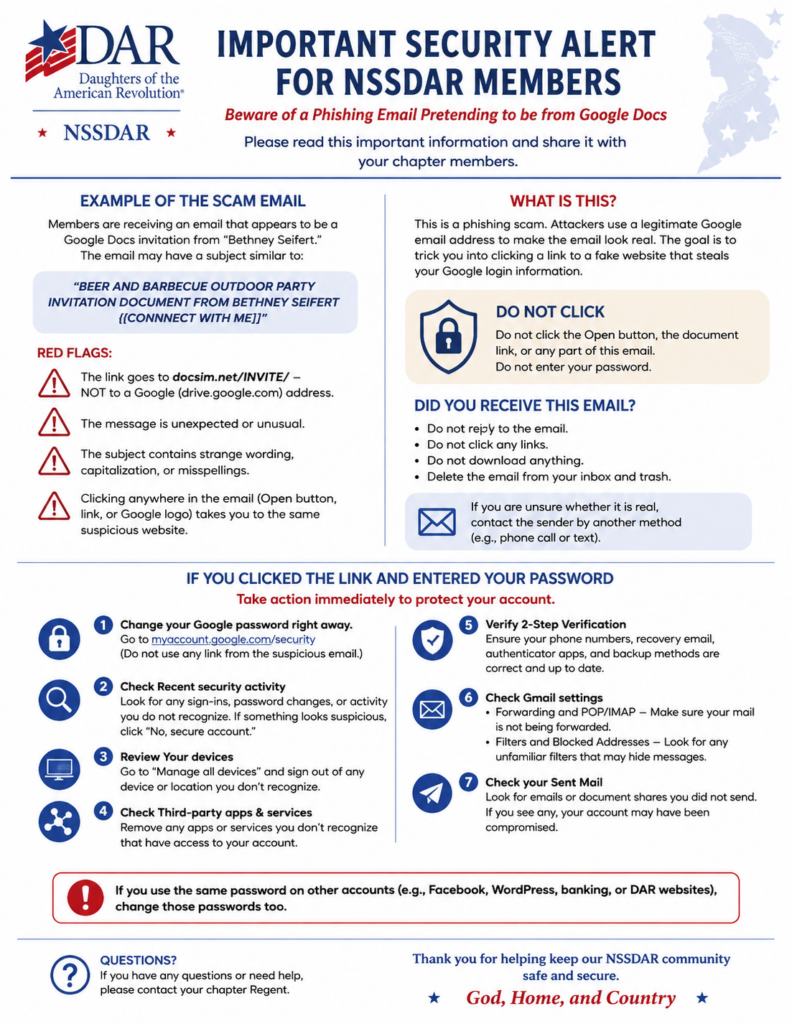
We want to make you aware of phishing emails currently circulating among our members. At this time, we know of at least two suspicious email messages that have been sent. These messages may appear to come from someone you know and may include a document-sharing notice, invitation, link, or request to forward information.
Please DO NOT CLICK on invitation links, open unexpected shared documents, or forward emails from members unless you have independently confirmed that the sender intended to send the message.
As a precaution, we strongly encourage everyone to review the security of their email account and change their email password, especially if you clicked a suspicious link or entered login information. Use a strong, unique password and enable two-factor authentication (2FA) whenever possible. You can also review your email account’s recent security activity and signed-in devices through your email provider’s security settings.If you receive an unexpected message from another DAR member, contact that person separately by phone, text, or a new email message before opening anything.
Phishing attacks are designed to look legitimate and often use the name of someone you recognize to gain your trust. Please remain cautious, even when a message appears to come from a fellow DAR member. If you receive a suspicious email, do not reply, click links, download attachments, or forward it to others. Instead, use your email provider’s Report Phishing or Report Spam option and delete the message. Taking a few extra moments to verify a message can help protect both your personal information and our entire NSSDAR community.
Thank you for helping keep our members safe online.